OWASP Top 10 Mitigation and Web Application Hardening in Laravel 13
Security is not an afterthought; it is a foundational architectural principle that must be designed into every layer of software.
1. Input Validation & SQL Injection Prevention
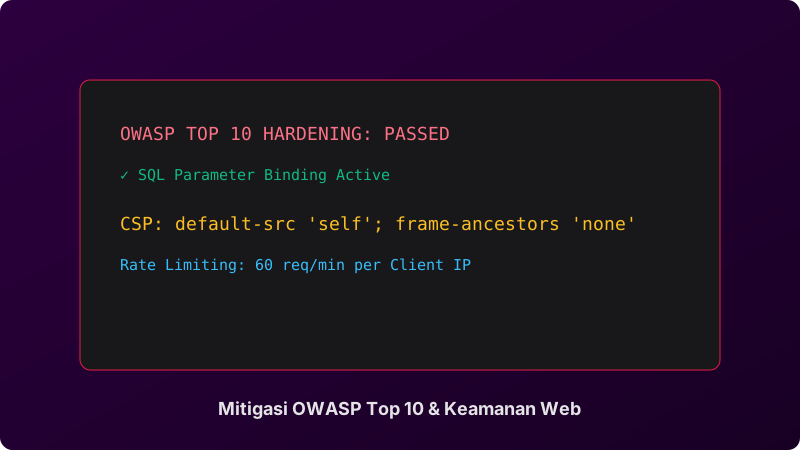
Eloquent ORM uses PDO parameter binding by default. Always avoid raw string concatenations in database queries:
// Insecure:
// DB::select("SELECT * FROM users WHERE email = '$email'");

// Secure parameter binding:
$user = User::where('email', $request->validated('email'))->first();
2. Broken Object Level Authorization (BOLA) Mitigation
Enforce strict ownership and role verification using Laravel Policies:
public function update(User $user, Project $project): bool
{
    return $user->id === $project->user_id;
}
Enforce in Controller actions via $this->authorize('update', $project).
3. Defense-in-Depth HTTP Headers & Throttling
Adopt Content Security Policy (CSP) headers, strict HSTS, and request throttling on public endpoints:
RateLimiter::for('api', function (Request $request) {
    return Limit::perMinute(60)->by($request->user()?->id ?: $request->ip());
});
Summary
A defense-in-depth security mindset shields web APIs and mission-critical applications against sophisticated real-world exploits.